
Automate access from day one to day done.
Turn identity changes from your systems of record into governed access decisions. SecurEnds automates onboarding, job changes, transfers, and offboarding using identity metadata, provisioning policies, Access Templates, configurable workflows, and auditable fulfillment.
Joiner, mover, leaver is really about responding to identity change.
Every identity has a lifecycle. The governance challenge is determining what should happen to access when that lifecycle changes—and executing those changes consistently without relying on someone to remember to submit a manual request.
Joiner — Onboarding
An identity enters the organization or a governed population. SecurEnds can evaluate authoritative metadata and determine the appropriate baseline access for that identity.
Mover — Change
A promotion, transfer, department change, job-title change, location change, or other attribute update can require existing access to be removed, retained, or replaced with new access.
Leaver — Offboarding
A separation can trigger account disablement, entitlement removal, deprovisioning, or account deletion according to the organization's offboarding policy and workflow.
Manual lifecycle management creates delay, inconsistency, and access risk.
Day-one delays
New hires may wait for managers or IT teams to identify and manually request the access required to become productive.
Access does not follow change
When someone changes roles or departments, new access may be added while old access remains, increasing privilege over time.
Slow offboarding
Manual termination processes can leave accounts or permissions active longer than the organization's policy intends.
Different systems, different processes
Identity data, approvals, application provisioning, and exception handling may be distributed across HR, IT, security, and application teams.
Human error
Spreadsheets, tickets, emails, and manual interpretation make consistent access decisions difficult to scale.
Difficult audit reconstruction
Organizations need to demonstrate why access changed, which policy triggered it, what was approved, and whether fulfillment completed successfully.
Let identity data drive lifecycle events—then let policy drive access.
SecurEnds connects lifecycle automation to authoritative identity metadata. Changes from HR systems, directories, IdPs, and other systems of record can be evaluated by provisioning policies and mapped to governed Access Templates and workflows.
From system-of-record change to governed fulfillment.
Ingest Identity Data
Connect systems of record and bring identity attributes into SecurEnds.
Detect Change
Identify new identities or changes to existing identity metadata.
Evaluate Policy
Provisioning policies evaluate configured conditions against the identity.
Run Workflow
Apply approvals, prerequisite checks, wait steps, and other business controls.
Fulfill & Audit
Add, change, or remove access and capture the complete action under a Request ID.
SecurEnds Identity Lifecycle Dashboard
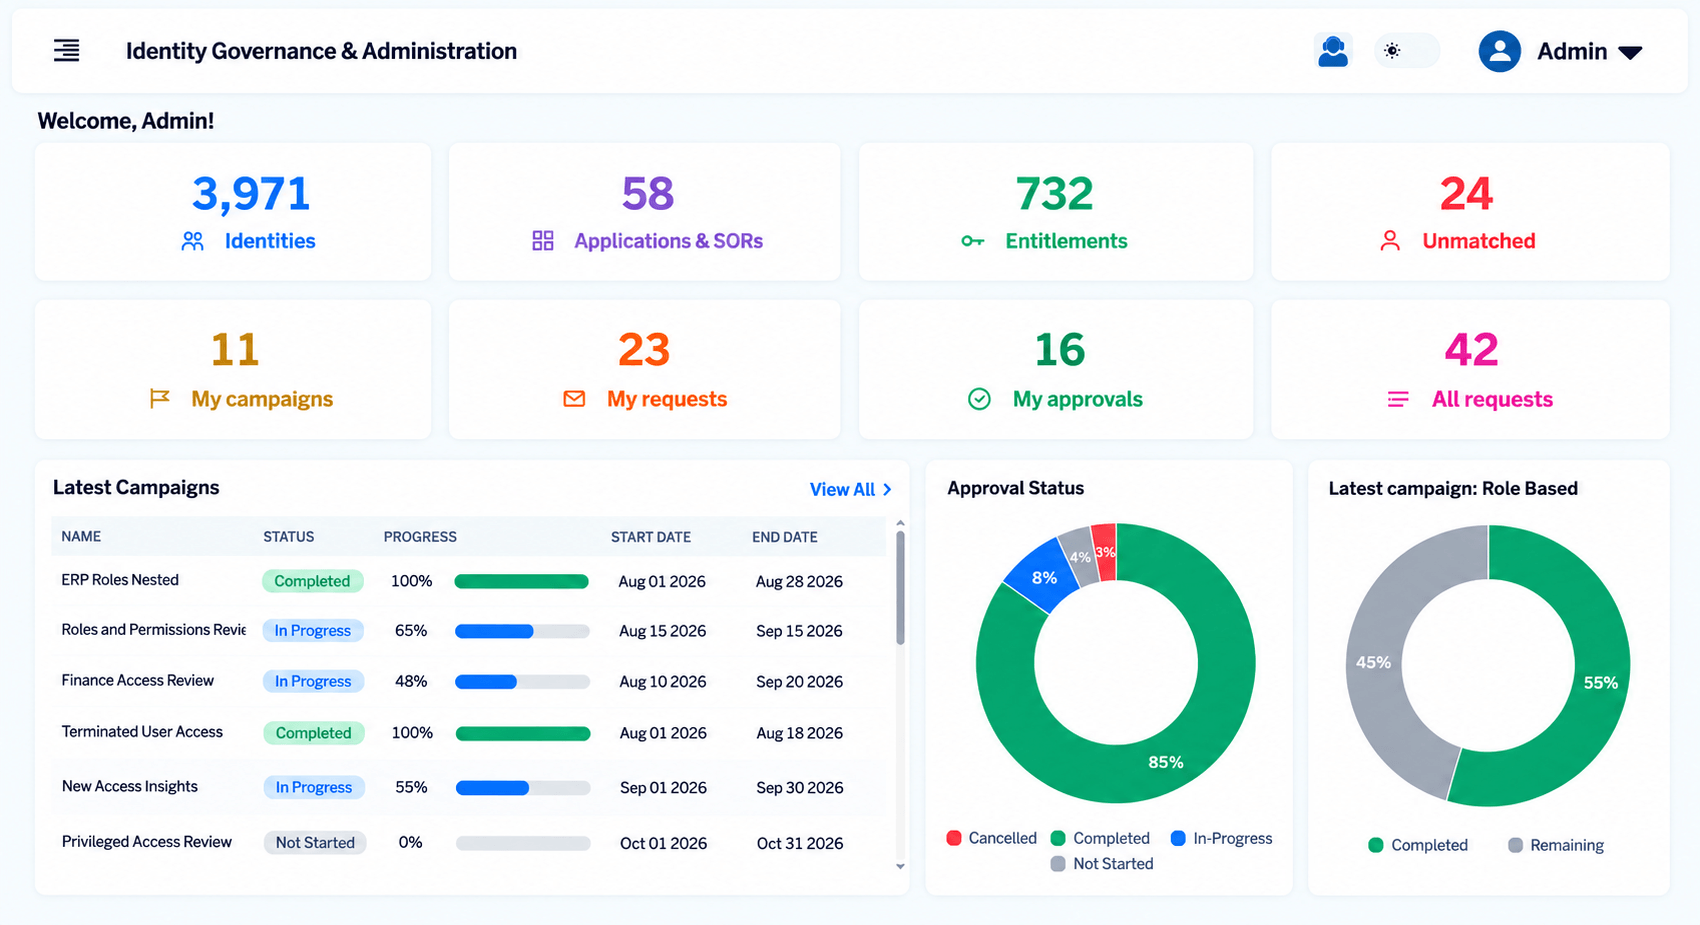
Use the attributes you already maintain to automate access decisions.
SecurEnds supports multiple systems of record and uses its data-ingestion capabilities to establish the identity context required for lifecycle automation.
Active Directory
Identity providers
Other authoritative sources
Modify
Disable
Deprovision
System-of-Record Integration
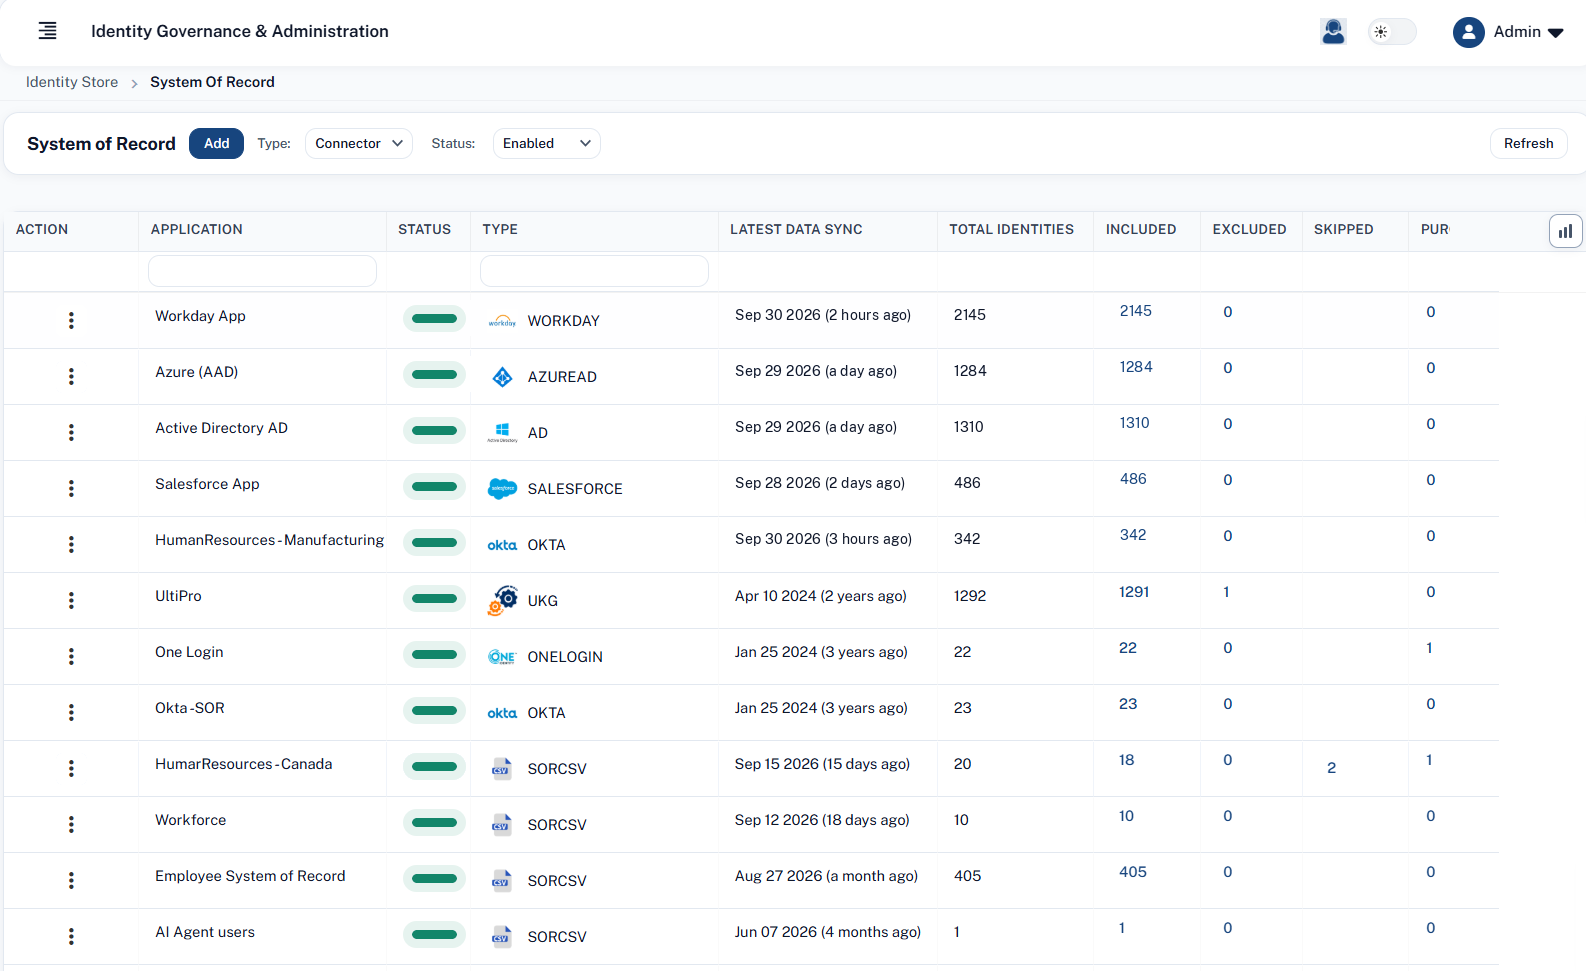
Translate identity conditions into automated access actions.
Provisioning policies are the decision layer between identity events and access. Each policy can evaluate one or more identity conditions, associate the matching population with one or more Access Templates, and execute a configurable workflow before fulfillment.
IF — Identity Conditions
THEN — Access Template
GOVERN — Workflow
SecurEnds Provisioning Policy
Replace with the actual policy configuration screen showing conditions, associated Access Templates, and workflow configuration.
Automate baseline access without abandoning least privilege.
Lifecycle automation works best when the organization first understands what access should be systematically assigned. SecurEnds Access Analysis can help organizations identify access patterns and establish governed Access Templates for birthright, department, location, job, or other RBAC structures.
Lifecycle policies can then use those approved templates to assign appropriate baseline access automatically, while additional or temporary access can continue through the SecurEnds Access Request process.
Day-one foundational access.
Job, department, location, or other approved access.
Additional access requested only when needed.
Build business controls directly into the lifecycle workflow.
Not every lifecycle event should immediately provision or deprovision access. SecurEnds workflows can introduce the required steps before the final action occurs.
Require an approval before selected lifecycle-driven access is fulfilled.
Hold provisioning until required training or another organizational prerequisite has been completed.
In healthcare or other regulated environments, incorporate required credential or qualification checks before access is granted.
Where policy permits, insert a configured wait step before selected offboarding actions are executed.
Lifecycle Workflow Configuration
Use the actual SecurEnds workflow screen here to demonstrate approvals, prerequisite steps, wait steps, and fulfillment actions.
One policy framework for the identity events that matter.
New Hire / New Identity
Detect the new identity, evaluate its metadata, assign the appropriate Access Templates, execute required workflow steps, and provision approved baseline access.
Job or Department Change
Use updated metadata to determine whether the identity should gain new role-based access and whether previous access should be removed.
Location or Cost-Center Change
Respond to organizational attributes that affect which applications, roles, groups, or permissions are appropriate.
Termination / Separation
Trigger governed disablement, deprovisioning, entitlement removal, or account deletion based on the configured offboarding process.
Non-Employee Lifecycle
Apply policy-driven lifecycle controls to contractors or other non-employee identities using the relevant authoritative data.
Service & Privileged Accounts
Extend lifecycle governance to account types beyond traditional employees when the required source data and lifecycle conditions are available.
Automation should improve auditability—not hide it.
REQ-20841
The system initiates the lifecycle action on behalf of the identity based on the detected source event and applicable provisioning policy.
System InitiatedMover EventWhat changed in the system of record?
Whose lifecycle event triggered the action?
Which provisioning policy and conditions matched?
What governed access was added or removed?
Which approvals, checks, or wait steps executed?
What was provisioned, disabled, removed, or deprovisioned?
Lifecycle Request & Audit Detail
Replace with a SecurEnds screenshot showing the Request ID, source event, workflow status, and provisioning/deprovisioning results.
Analyze. Define. Automate. Request. Review.
SecurEnds connects Access Analysis, governed Access Templates, Identity Lifecycle Management, Access Request, and access-review processes into a broader identity-governance model—helping organizations automate predictable access while retaining governance over exceptions and change.
Make identity change operationally simple and security-aware.
Faster Day-One Access
Use authoritative identity data and policy to initiate appropriate baseline access without waiting for repetitive manual requests.
Reduce Access Accumulation
Respond to mover events by evaluating what access should change rather than continually adding privileges as employees move through the organization.
Consistent Offboarding
Turn separation events into defined workflows for disabling, removing, deprovisioning, or deleting access.
Less Manual Administration
Reduce repetitive interpretation, ticket creation, and coordination across HR, IT, security, and application teams.
Flexible Business Controls
Add approvals, prerequisite checks, waiting periods, and other workflow steps where automation requires human or business validation.
Auditability by Design
Connect the source event, policy decision, workflow, access change, and fulfillment status through a traceable Request ID.
Turn identity changes into governed access changes.
See how SecurEnds can automate joiner, mover, and leaver processes using system-of-record data, provisioning policies, Access Templates, configurable workflows, and auditable fulfillment.
© SecurEnds — Identity Lifecycle Management website content concept. Product screenshots and final brand styling can be inserted before publication.