Virginia Agency Access Governance
COV RAMP Approved Identity Governance Built for Virginia Agencies
Review, understand, and control access across agency applications, Active Directory, databases, contractors, service accounts, and AI agents — without spreadsheets or guesswork.
COV RAMP Approved, SOC 2 Type II, and TX-RAMP Authorized
Designed around how public sector audits actually evaluate access
Covers employees, contractors, vendors, service accounts, and AI agents
COV RAMP Approved
Commonwealth of Virginia
SOC 2 Type II
Independent control audit
TX-RAMP Authorized
Public sector ready
Virginia Agency Experience
VDH implementation scope

Controls Exist. Decisions Break Down.
Most Virginia agencies have the right controls in place:
Access reviews are completed
Security policies are documented
Applications have owners
But during audits and incidents, the gaps appear:
Reviewers do not understand technical entitlements
AD groups are approved without context
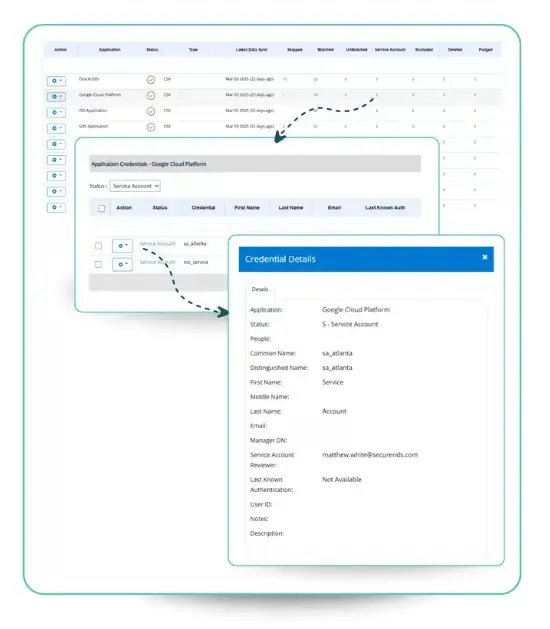
Service accounts are not consistently reviewed
Access persists after role changes or separation
This is not a control problem. It is a decision problem.
SecurEnds supports the decision — not just the control documentation.
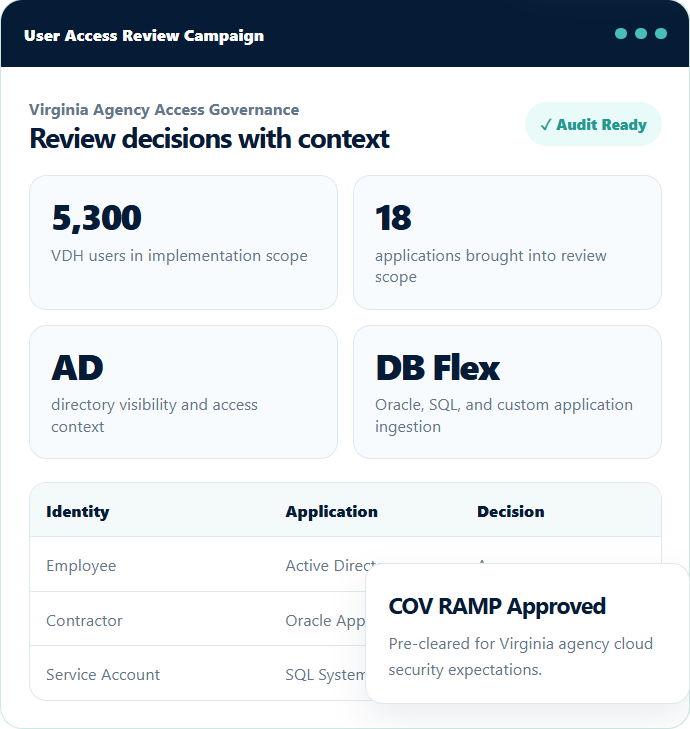
VDH Sustains Access Governance Across Public Health Systems
SecurEnds helps the Virginia Department of Health manage access governance across 5,300 users and 18 applications, spanning Active Directory, Oracle-based systems, SQL-based systems, and public health platforms.
The outcome: centralized entitlement ingestion, automated UAR campaigns, and audit-ready reporting across a complex public health environment.
Modern access reviews turn fragmented data into accountable decisions.
Start Where Auditors Start:
User Access Reviews
Cross-System Visibility
Aggregate access across AD, databases, applications, and custom systems.
Reviewer-Friendly Decisions
Present users, roles, accounts, and entitlements in one place.
Automated Campaigns
Enable approve, revoke, and remediation decisions with context.
Audit-Ready Reports
Generate audit-ready evidence automatically for reviews and oversight.
Before vs After
Before SecurEnds
Access reviews in spreadsheets
Application permissions not understood
AD groups reviewed blindly
Service accounts unmanaged
Audit prep takes weeks
With SecurEnds
Single view across systems
Reviewer-friendly access context
Automated review campaigns
Service accounts and AI identities governed
Audit-ready reporting available on demand
How SecurEnds Works
Connect Systems
Active Directory, HR, databases, applications, APIs, and files.
Normalize Access
Translate entitlements into business-readable context.
Launch Reviews
Automated campaigns across users and service accounts.
Enforce Decisions
Approve and revoke actions trigger workflows and fulfillment.
Generate Evidence
Full audit trails for reviews, reporting, and oversight.
Build Beyond User Access Reviews
Onboarding & Offboarding
Automate joiner, mover, and leaver workflows across users, systems, and applications.
IT Risk
Identify access risk, toxic combinations, and control gaps across the identity landscape.
Vendor Risk
Strengthen third-party access oversight with clearer visibility, reviews, and accountability.
AI Agent
Extend identity security to AI agents with accountability, oversight, and policy-based control.