
Cybersecurity Risk Assessments, Governance, and Compliance Management
Assess IT, cloud, and vendor risk with prebuilt control libraries, route every question to the right owner, and hand auditors’ proof of compliance in one click.
Compliance shouldn't depend on who still has the spreadsheet
Most risk assessments still run on spreadsheets and email. When the auditor arrives, your team rebuilds the year from scratch.
Separate spreadsheets for NIST, HIPAA, FFIEC, and SOC 2, each asking the same teams the same questions.
Screenshots and documents scattered across inboxes and shared drives, with no link to the control they prove.
Risks get logged, then stall when the owner changes roles or leaves the organization.
From first assessment to audit report in five steps
No implementation project. The base product arrives with a business hierarchy, workflows, and NIST-mapped questionnaires already configured.
Start with a template
Pick a prebuilt questionnaire mapped to NIST, HIPAA, FFIEC, and more, or build your own.
Launch a campaign
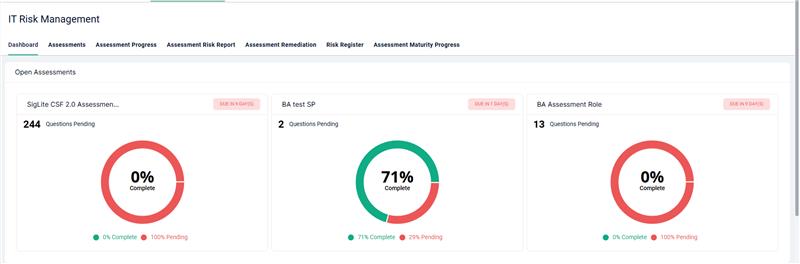
Schedule it and assign full questionnaires or single questions to people, groups, or roles.
Collect evidence
Participants get an email invite to answer, comment, and upload supporting documents.
Remediate
Push findings to Jira or ServiceNow with owners and due dates, then track them to closure.
Prove it
Produce proof of compliance and executive dashboard reports in one click.
Everything a risk program needs, without a year-long rollout
Zero setup
Start on day one with prebuilt control templates, workflows, and inventory already configured.
Customizable controls library
One unified template aligned with NIST CSF, 800-53, ISO 27001, HIPAA, and more cuts duplicate questionnaires.
Assessment campaigns
Schedule campaigns for set timeframes and include as many assessments as you need.
Centralized evidence
Every file is categorized, mapped to its control, and reusable across the organization.
Automated control ownership
When someone changes roles, their controls and questionnaires are reassigned automatically.
ITSM remediation
Real-time ticket assignment and tracking through Jira, ServiceNow, and other ITSM systems.
Risk-informed decisions
Monitor outliers when scores exceed thresholds or regulations change, and direct resources to the highest risks.
Drill-down reporting
Break down risk by score, control, department, and remediation owner.
Integrated platform
Connect business, security, and IT teams around the same requirements, policies, and results.
Your frameworks, ready on day one
Every subscription includes prebuilt control sets and questionnaires, updated for current threats like ransomware.
Security frameworks
Industry regulations
Privacy
Threat-focused
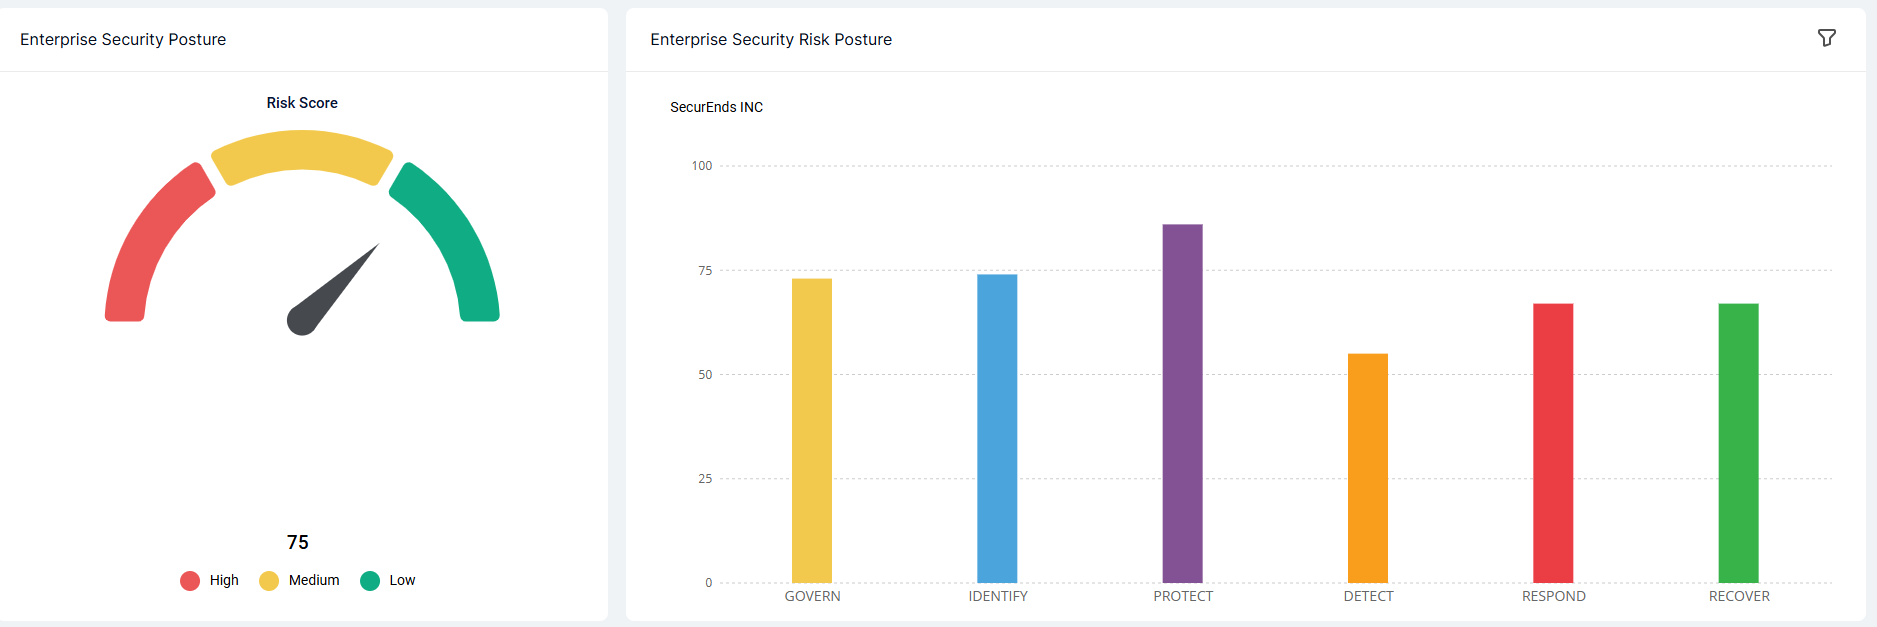
See your security posture in one number
From the first control questionnaire to the board report, every step lives in SecurEnds. SecurEnds rolls up control measurements from every assessment into an enterprise security posture score, then lets you drill into what's moving it.
Start with one module. Add the rest in a click.
Every module shares the same controls, evidence, and reporting, so your program grows without starting over.
IT cybersecurity risk assessment
Assess applications, assets, and business units against your frameworks and track your posture over time.
Third-party risk management
Tier, assess, score, and monitor vendors with a central repository of findings, evidence, and history.
Cloud and SaaS compliance
Check Microsoft 365, Azure, AWS, and GCP configurations against compliance requirements.
Risk management
Keep an enterprise risk register with owners, severity, treatment, and status.
Policy management
Manage policies alongside the controls and evidence that prove they're followed.
Privacy management
Organize privacy assessments and records that support GDPR and CCPA obligations.
Bring AI agents into your governance program
AI agents now act across your systems, which makes them a compliance question too. Nexus AI Governance gives every agent an identity, visible activity, and enforced policy.
Inventory every AI agent alongside human and non-human identities.
See what agents are doing across your environment in real time.
Control what each agent is allowed to do, action by action.
Why CISOs choose SecurEnds GRC
Many customers come to SecurEnds after struggling with expensive, heavily customized GRC suites that never delivered the value they expected.
| SecurEnds GRC | Traditional GRC suites | |
|---|---|---|
| Time to first assessment | Within 24 hours of subscribing | Often a services-led implementation |
| Try before you buy | Fully functional 14-day trial | Typically a sales-led evaluation |
| Framework content | 15+ control sets and questionnaires included | Frequently configured per project |
| Control ownership | Reassigned automatically when roles change | Usually maintained manually |
| Identity governance | Access reviews on the same platform | Typically a separate identity tool |
| Buying model | Modular, add capabilities as you grow | Often a broad platform commitment |
How ready is your program, really?
Answer four questions and see where auditors and examiners are most likely to find gaps. It takes about two minutes.
Yes
No
Yes
Yes
Still deciding? Talk to our team.
How fast can we get started?
Most customers are using SecurEnds within 24 hours of subscribing. The base product comes preconfigured with a business hierarchy, workflows, and questionnaires mapped to NIST controls.
Can we try it before buying?
Yes. We offer a fully functional 14-day trial of IT Risk Assessment, Third-Party Vendor Risk Management, and Cloud and SaaS Compliance. You can keep using the product by subscribing when the trial ends.
Which control sets are included?
Every subscription includes NIST CSF, NIST SP 800-53 r5 and r4, NIST SP 800-171 r2, HIPAA, GDPR, CCPA, FFIEC, CMMC, and third-party questionnaires, plus questions mapped to PCI DSS, ISO 27001, and SOC 2. Threat-focused questionnaires, such as ransomware readiness, are also included.
How many assessments can a campaign include?
As many as you need. Any assessment template built for an inventory item with a customizable control set can be added to a campaign.
Does SecurEnds integrate with our ticketing tools?
Yes. Out-of-the-box integrations with Jira, ServiceNow, and other ITSM systems let you assign and monitor remediation tickets in real time.
Is SecurEnds GRC customizable?
Yes. Control libraries, questionnaires, templates, and campaign assignments can all be tailored, and the modular platform lets you add capabilities as your program grows.
Do you support SSO?
Yes. Users can sign in with Microsoft 365 or Google accounts.
How is customer data secured?
SecurEnds GRC uses enterprise-grade security at every layer and is hosted on Amazon Web Services.
How much does it cost?
Pricing depends on the modules you choose, with options for organizations and managed service providers. Our team offers a no-pressure consultation to help you pick the right fit.
Run your first risk assessment tomorrow
Start with a prebuilt NIST template, invite your control owners, and see your security posture score within your free trial.
Fully functional trial. Talk to sales about modules and pricing.